In this Lightboard Post of the Week, I answer a question about 2FA and SSO with AD/RSA on BIG-IP by creating a SSO Credential Mapping policy agent in the Visual Policy Editor, that takes the username and password from the logon page, and maps them to variables to be used for SSO services. Special thanks to senthil147 for the question and a new 2018 MVP, MrPlastic (Lee Sutcliffe, which I flubbed) for the great answer.
Posted Question on DevCentral: https://devcentral.f5.com/questions/2fa-authentication-with-sso-on-apm-57581
ps
Showing posts with label sso. Show all posts
Showing posts with label sso. Show all posts
Friday, January 26, 2018


Tuesday, November 14, 2017
VDI Gateway Federation with BIG-IP
Today let’s look at how F5 BIGIP APM can consolidate, secure and federate all
the core VDI gateways technology. For instance, if an organization decides move
from one VDI technology to another or if you’re consolidating VDI technologies,
BIG-IP can help.
On the BIG-IP we’ve set up three VDI environments. Microsoft RDS/RDP with a broker authentication server, VMware Horizon and Citrix ZenApp. With only a corporate account, a user can authenticate to all of them as needed and access all available desktop content.
In this example, we connect to the BIG-IP APM. This is the default view.

And here we’ve put some advanced security fields like OTP or multifactor authentication for instance.


With a single, multifactor authentication we’re able to gain access to our federated BIG-IP Webtop and select the specific VDI resource we need.
From an administrative view, here is the full Visual Policy Editor (VPE) for
the overall solution. This also shows where the OTP/Grid is if you follow the
Host FQDN path.


Special thanks to F5 Sr. Security SE Matthieu Dierick for the
explanation and you can watch the demo video.
ps
On the BIG-IP we’ve set up three VDI environments. Microsoft RDS/RDP with a broker authentication server, VMware Horizon and Citrix ZenApp. With only a corporate account, a user can authenticate to all of them as needed and access all available desktop content.
In this example, we connect to the BIG-IP APM. This is the default view.

And here we’ve put some advanced security fields like OTP or multifactor authentication for instance.

So here we’d use our username and password and for additional security we'll
choose a secondary grid. By default, a grid is not generally available from any
of the VDI vendors. When we select grid, BIG-IP APM will present a grid for a
PIN entry. This is provided through a partnership with Gemalto. BIG-IP is connecting to Gemalto
servers to present the grid to the user. We then enter our confidential PIN.

Upon auth, we’re presented with our BIG-IP APM Webtop and BIG-IP did the
necessary single sign on for all the VDI technologies and environments assigned
to us.

With a single, multifactor authentication we’re able to gain access to our federated BIG-IP Webtop and select the specific VDI resource we need.

And here are the specific inspections and criteria for the VDI scenario. You can
see a path for each VDI vendor along with specific inspections and actions
depending on the situation.

Tuesday, October 10, 2017
Legacy Application SSO with BIG-IP and Okta
IT organizations have a simple goal: make it easy for workers to access all
their work applications from any device. But that simple goal becomes
complicated when new apps and old, legacy applications do not authenticate in
the same way.
Today we’ll take you through BIG-IP APM’s integration with Okta, a cloud-based identity-as-a-service provider.
The primary use case for this scenario is providing the user authentication through Okta and then Okta providing BIG-IP APM a SAML assertion so that BIG-IP can perform legacy SSO using either Kerberos Constrained Delegation (KCD) or Header Authentication. BIG-IP is the Service Provider (SP) in this SAML transaction.
As we log on to a BIG-IP, you’ll see that we have two policies/application examples.

Let’s click on the Edit button under Access Policy for app1-saml-sp-okta.
This takes us to the Visual Policy Editor (VPE) for the first application. As
the chart flows, BIG-IP is consuming the SAML authentication, then storing the
SSO credentials and doing a Variable Assign so we know who the user is.

The next entry, app3-saml-sp-okta, looks very similar.

One of the things that is different however is for Header Authentication,
we’re using a Per Request Policy. You can view/configure this by going to Access Policy>Per Request Policy.

We click Edit (under Access
Policy) and here via the flow, the user enters and on every request, we’re
going to remove the Okta header name, which is arbitrary and doesn’t need to be
that value – could be any value you choose. But we want to make sure that no
one is able to pad that header into a request. So, we’ll remove it and insert
the variables BIG-IP receives from Okta. This way the application can consume
it and we know who that user is.

So, what does it look like.
First, we’ll log into Okta and in the portal, we see two applications – the Header Auth and Kerberos Auth.

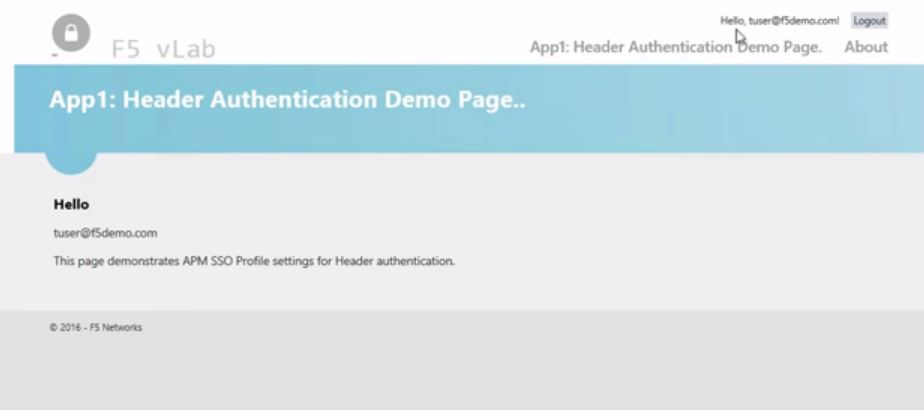
We’ll test the Header authentication first and see that we’re logged into
App1 using Header authentication. Tuser@f5demo.com
was the account we logged into with Okta and we see the application has been
single-signed into using that credential.

Now let’s hit that Kerberos auth application. Here again, we’ve been SSO’d
into the application. You may notice that the user looks a bit different here
as F5DEMO\tuser since this time we used Kerberos Constrained Delegation. So,
we’ve obtained a Kerberos ticket from the domain controller for F5DEMO as the
user to use. So the username can look a little different but it’s mainly about
formatting.

BIG-IP is able to consume that SAML assertion from Okta and then use SSO capabilities via Header or Kerberos for legacy applications. Watch Cody Green’s excellent demo of this integration.
ps
Today we’ll take you through BIG-IP APM’s integration with Okta, a cloud-based identity-as-a-service provider.
The primary use case for this scenario is providing the user authentication through Okta and then Okta providing BIG-IP APM a SAML assertion so that BIG-IP can perform legacy SSO using either Kerberos Constrained Delegation (KCD) or Header Authentication. BIG-IP is the Service Provider (SP) in this SAML transaction.
As we log on to a BIG-IP, you’ll see that we have two policies/application examples.


First, we’ll log into Okta and in the portal, we see two applications – the Header Auth and Kerberos Auth.


BIG-IP is able to consume that SAML assertion from Okta and then use SSO capabilities via Header or Kerberos for legacy applications. Watch Cody Green’s excellent demo of this integration.
ps
Wednesday, July 26, 2017
Lightboard Lessons: What is BIG-IP APM?
In this Lightboard, I light up some lessons on BIG-IP Access Policy Manager. BIG-IP APM provides granular access controls to discreet applications and networks supporting 2FA and federated identity management. You can also check out Chase's written article What is BIG-IP APM?
ps
ps
Tuesday, February 14, 2017
Shared Authentication Domains on BIG-IP APM
How to share an APM session across multiple access profiles.
A common question for someone new to BIG-IP Access Policy Manager (APM) is how do I configure BIG-IP APM so the user only logs in once.
By default, BIG-IP APM requires authentication for each access profile.

This can easily be changed by sending the domain cookie variable is the access profile’s SSO authentication domain menu.
Let’s walk through how to configure App1 and App2 to only require authentication once.
We’ll start with App1’s Access Profile.

Once you click through to App1’s settings, in the Top menu, select SSO/Auth Domains.

For the Domain Cookie, we’ll set the value to f5demo.com since App1 and App2
use this domain and it is a FQDN. Of course, click Update.
Next, we’ll select App2’s Access Profile. Like App1, we select SSO/Auth Domains and set the Domain Cookie value to f5demo.com.
To make sure it works, we’ll launch App1 in our browser.


Granted this was a single login request for two simple applications but it
can be scaled for hundreds of applications. If you‘d like to see a working demo
of this, check it out
here.
ps
A common question for someone new to BIG-IP Access Policy Manager (APM) is how do I configure BIG-IP APM so the user only logs in once.
By default, BIG-IP APM requires authentication for each access profile.

This can easily be changed by sending the domain cookie variable is the access profile’s SSO authentication domain menu.
Let’s walk through how to configure App1 and App2 to only require authentication once.
We’ll start with App1’s Access Profile.

Once you click through to App1’s settings, in the Top menu, select SSO/Auth Domains.

Next, we’ll select App2’s Access Profile. Like App1, we select SSO/Auth Domains and set the Domain Cookie value to f5demo.com.

We’re prompted for authentication and enter our credentials and luckily, we have
a successful login.

And then we’ll try to login to App2. And when we click it, we’re not prompted
again for authentication information and gain access without prompts.

Wednesday, December 14, 2016
Lightboard Lessons: SSO to Legacy Web Applications
IT organizations have a simple goal: make it easy for workers to access all
their work applications from any device. But that simple goal becomes
complicated when new apps and old, legacy applications do not authenticate in
the same way.
In this Lightboard Lesson, I draw out how VMware and F5 helps remove these complexities and enable productive, any-device app access. By enabling secure SSO to Kerberos constrained delegation (KCD) and header-based authentication apps, VMware Workspace ONE and F5 BIG-IP APM help workers securely access all the apps they need—mobile, cloud and legacy—on any device anywhere.
ps
Related:
In this Lightboard Lesson, I draw out how VMware and F5 helps remove these complexities and enable productive, any-device app access. By enabling secure SSO to Kerberos constrained delegation (KCD) and header-based authentication apps, VMware Workspace ONE and F5 BIG-IP APM help workers securely access all the apps they need—mobile, cloud and legacy—on any device anywhere.
ps
Related:
Tuesday, July 5, 2016
Q/A with Yann Desmarest - DevCentral's Featured Member for July

And one of his favorite activities is developing complex iRules and that’s why he is DevCentral's Featured Member for July!
We got a chance to chat with Yann about his work, his life and why he enjoys participating in the DevCentral Community.
DevCentral: Hi Yann. Thanks for your time. You’ve been a tremendous contributor to the DevCentral community over the years and wondered what keeps you involved?
Yann: I’m always looking for new challenges and DevCentral is a really good place to solve complex issues and to share knowledge and experiences with peers. It’s also a place that I can find useful information on iControl, iRules and iApps code.DC: Tell us a little about the areas of BIG-IP expertise you have.
YD: At my earliest stage in the business world, I was involved on basic BIG-IP LTM projects. After some successful experiences, I wondered if I could rise up to another level and decided to learn BIG-IP ASM, APM and GTM modules as well.DC: You often participate and post in the Codeshare area – tell us about some of your favorite submitted iRules/iApps and how they work.
Now, I think I’m pretty comfortable with all F5 BIG-IP modules but I’m clearly specialized in security and more precisely the authentication and WebSSO part delivered by BIG-IP APM.
I also acquired some development skills using iRules and iControl.
YD: I've had several requests to protect Microsoft Skype for Business Edge services against NTLM brute force and dos attacks. I decided to develop an iRule to intercept the encrypted traffic and identify NTLM authentication attempts on the SIP flow. Then, suspicious IPs and users are blacklisted for a duration that you can define in the RULE_INIT event.DC: Describe one of your biggest BIG-IP challenges and how DevCentral helped in that situation.
I had also requirements to provide Client certificate authentication on Microsoft Exchange ActiveSync for Apple iOS devices. The main issue is that this kind of authentication requires a Mobile Device Management or Apple Configurator system. Deploying a full MDM for that need may be overkill so we developed an iRule that provisions the Exchange payload to the iOS device. The client certificate is retrieved using SCEP protocol. Now, with the availability of iRulesLX, I will be able to extend this feature to retrieve a certificate using third party APIs.
And finally my favorite is the APM Full Step Up Authentication iRule and Access profile that we published on DevCentral. I had a look at the Step-Up authentication feature on the APM v12.1.0 and found that it’s currently limited. I decided to develop my own configuration to make it more flexible and mainly to have this feature available for older BIG-IP versions. No doubt that my configuration will be deprecated in future releases because APM will enhance its own feature set.
I have many more iRules, iApps and iControl scripts to share with the community in the future.
DC: Lastly, if you weren’t an IT admin – what would be your dream job? Or better, when you were a kid – what did you want to be when you grew up?YD: I had a requirement to integrate APM with an iOS and Android mobile application. The application use SOAP body to POST credentials and a second factor was required for external users. I had to intercept the SOAP body to retrieve the username and password, then play those credentials through an external REST API web service and if the user is connecting from a public IP address, prompt the end user for a second factor that I send to a third party web gateway. This is a lot of peers and exchanges to integrate in the authentication process. I had also to implement full SOAP responses and handle errors. I consulted DevCentral and the iRules wiki to find how to use sideband connections, ifiles, ACCESS events and some crypto commands. Without the DevCentral community, I would not have been able to face this challenge.

YD: Computer science was part of my life since the very beginning. Later, I decided to be an IT expert, to solve complex challenges and to help people securing their environments. Now, I’m following my dreams and work hard to be a computer expert.
Just few words to thank all my colleagues and our F5 Field System Engineers that help me a lot to acquire more skills and experience on F5 technologies.
DC: Thanks Yann! Check out all of Yann’s DevCentral contributions and follow him @expertsolch
Wednesday, March 6, 2013
Pulse2013 – IBM Maximo Optimization & SSO with BIG-IP APM
It’s an all Nojan week at the Pulse2013 conference at the MGM Grand! This time, he shows Peter Silva how to deploy Maximo Asset Management with the new Maximo iApp from F5 found on DevCentral along with how to configure acceleration and SSO for Maximo users. Increased performance for remote users along with the ease of deployment for administrators. Got Maximo? Get BIG-IP APM.
ps
Related:
- Pulse2013 - Find F5
- Pulse2013 – Gimme 90 Seconds: IBM Edition
- Pulse2013 – BIG-IP ASM & IBM InfoSphere Guardium
- IBM Pulse2013 Conference
- InfoSphere Guardium Data Security
- IBM Guardium Deployment Guide
- F5's YouTube Channel
- In 5 Minutes or Less Series (23 videos – over 2 hours of In 5 Fun)
- Inside Look Series
- Life@F5
Technorati Tags: f5,ibm,pulse,ibmpulse,psilva,video,security, sso,maximo, optimized
| Connect with Peter: | Connect with F5: |
  |    |
Tuesday, November 13, 2012
SharePoint Conference 2012: Secure Remote Access & SSO with BIG-IP APM
I catch Greg Coward, F5 Solution Engineer, to show how to configure BIG-IP APM to provide Secure Remote Access and SSO to #SharePoint. Yesterday we configured SharePoint with a F5 iApp and today we’re adding secure remote access to the deployment. #spc12
ps
Resources:
- SharePoint Conference 2012: Find F5
- SharePoint Conference 2012: Gimme 90 Seconds with James Hendergart
- SharePoint Conference 2012: Configuring SharePoint on BIG-IP
- SharePoint Conference 2012: The Top 7 Questions
- SharePoint Conference 2012: Secure Remote Access & SSO with BIG-IP APM
- Solutions for Microsoft SharePoint Server
- Securing Exchange and SharePoint
- In 5 Minutes or Less Series (22 videos – over 2 hours of In 5 Fun)
- F5 YouTube Channel
Technorati Tags: F5,big-ip,security,management,infrastructure,sharepoint,cloud,waf,tmg, analytics,psilva,video
| Connect with Peter: | Connect with F5: |
 | |
SharePoint Conference 2012: Secure Remote Access & SSO with BIG-IP APM
I catch Greg Coward, F5 Solution Engineer, to show how to configure BIG-IP APM to provide Secure Remote Access and SSO to #SharePoint. Yesterday we configured SharePoint with a F5 iApp and today we’re adding secure remote access to the deployment. #spc12
ps
Resources:
- SharePoint Conference 2012: Find F5
- SharePoint Conference 2012: Gimme 90 Seconds with James Hendergart
- SharePoint Conference 2012: Configuring SharePoint on BIG-IP
- SharePoint Conference 2012: The Top 7 Questions
- SharePoint Conference 2012: Secure Remote Access & SSO with BIG-IP APM
- Solutions for Microsoft SharePoint Server
- Securing Exchange and SharePoint
- In 5 Minutes or Less Series (22 videos – over 2 hours of In 5 Fun)
- F5 YouTube Channel
Technorati Tags: F5,big-ip,security,management,infrastructure,sharepoint,cloud,waf,tmg, analytics,psilva,video
| Connect with Peter: | Connect with F5: |
| | |
Friday, October 1, 2010
F5 Access Policy Manager & Oracle Access Manager Integration - Part 1
A couple days ago, I posted the F5 BIG-IP Access Policy Manager and Oracle Access Manager Integration demo video created by Chris Akker and narrated by Chris Manley – who does a great job, by the way. That was actually Part 2 of a longer video and was edited to show the actual admin GUI steps required to configure the BIG-IP Access Policy Manager for Oracle Access Manager integration on the BIG-IP. This video, Part 1, helps you understand the basics of both APM and OAM and the details of how Access Policy Manager and Oracle Access Manager are integrated. After this, (if you haven’t already) proceed to F5 BIG-IP Access Policy Manager and Oracle Access Manager Integration Part 2. :-)

ps
Technorati Tags: F5, infrastructure 2.0, integration, Pete Silva, security, business, education, technology, application delivery, cloud, virtualization, oracle, oow
twitter: @psilvas

Thursday, June 3, 2010
F5's BIG-IP with Oracle® Access Manager to enhance SSO and Access Control
Learn how F5's BIG-IP LTM/APM helps in conjunction with Oracle Access Manager centralizing web application authentication and authorization services, streamline access management, and reduce infrastructure costs Watch how BIG-IP APM can reduce TCO, lower deployment risk, and streamline operational efficiencies for customers along with having a unified point of enforcement to simplify auditing and control changes in configuring application access settings.
Subscribe to:
Posts (Atom)
